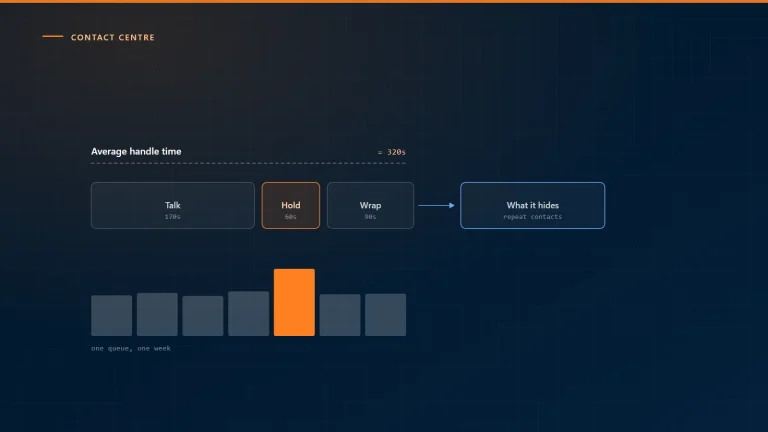
Average handle time tells you less than you think
AHT is the easiest contact center metric to move and the easiest to move the wrong way. What it measures, what it hides, and the three numbers to read beside it.
Controls, evidence and the audit preparation that goes with them.
Develop and place into place access restrictions and encryption-equipped safe cloud architectures.
By conducting audits and reporting, make sure that regulatory standards are being followed.
Quickly identify and address security threats to reduce their impact.
Get policies in place to safeguard data integrity and guarantee adherence to privacy laws.
To maintain security posture, proactive management and ongoing monitoring are required.
Create and execute incident response strategies to effectively address security breaches.
Secure cloud networks with firewalls, intrusion detection/prevention systems, and secure VPNs.
Make use of automation tools to expedite regulatory reporting procedures and perform compliance checks.
What auditors ask for, and what we put in place before they do.
Identify and Mitigate Risks
AcmaCorp carefully identifies weaknesses in your cloud infrastructure by doing thorough risk evaluations. Our methodology involves a comprehensive examination and assessment of possible risks, guaranteeing that every facet of your cloud infrastructure is closely examined for vulnerabilities. Through the utilization of techniques and methodologies, we provide practical insights and strategic recommendations that effectively manage risks.
Our objective is to protect your data integrity and business continuity by fortifying your cloud infrastructure against possible threats. Collaborate with AcmaCorp to improve the security posture of your cloud environment by utilizing professional risk assessment services that are customized to your company’s requirements.
Safeguarding Data Integrity
AcmaCorp prioritizes strong data protection methods to maintain the integrity, confidentiality, and privacy of your data in the cloud. To protect sensitive information from unwanted access and breaches, we use severe security processes such as modern encryption techniques and comprehensive access controls. Our solutions are designed to comply with severe data protection laws while minimizing the risk of data exposure.
AcmaCorp enables your firm to safely use cloud services while protecting data integrity and meeting legal standards by combining industry best practices with cutting-edge technologies. We can create comprehensive data security techniques that protect your data throughout its lifecycle in the cloud.
Rapid Detection and Response
AcmaCorp uses powerful threat detection capabilities to quickly detect and respond to security problems in your cloud environment. Our proactive monitoring systems look for anomalies and unusual activity on a continual basis, allowing us to discover possible risks early. We use real-time threat data and sophisticated analytics to ensure speedy response and mitigation measures, reducing downtime and protecting your business operations.
AcmaCorp rigorous security procedures and persistent monitoring enable your firm to ensure the integrity and availability of important cloud resources, hence improving overall security posture. We offers comprehensive threat detection solutions that protect your cloud infrastructure from growing cybersecurity threats.
Ensure Regulatory Compliance
AcmaCorp prioritizes compliance to industry rules and guidelines by providing comprehensive Cloud Security and Compliance Services that include exhaustive audits, ongoing monitoring, and detailed reporting. Our committed staff regularly assesses how well your cloud infrastructure complies with legal standards, offering thorough analysis and practical suggestions to close any gaps. We assists businesses in successfully navigating complicated regulatory environments by using rigorous compliance procedures and proactive risk management.
We support the implementation of essential controls, guaranteeing the continuous maintenance of data availability, confidentiality, and integrity. In order to quickly eliminate risks, our strategy entails not only detecting vulnerabilities but also suggesting and putting security solutions in place.
Sector experience shapes the answer as much as the technology does.
Every use case we have written, across the industries we build for — not only the ones that match this page. Each is a worked example: the problem as it usually appears, and the shape of the answer.
Browse every use caseISO 27001, SOC 2, PCI DSS, HIPAA and GDPR obligations are the common ones. The control work overlaps heavily between them, so mapping once against several frameworks is cheaper than treating each as a separate project.
We prepare you for certification and support the audit; the certificate is issued by an accredited body, not by us. Any supplier claiming to certify you directly is describing something else.
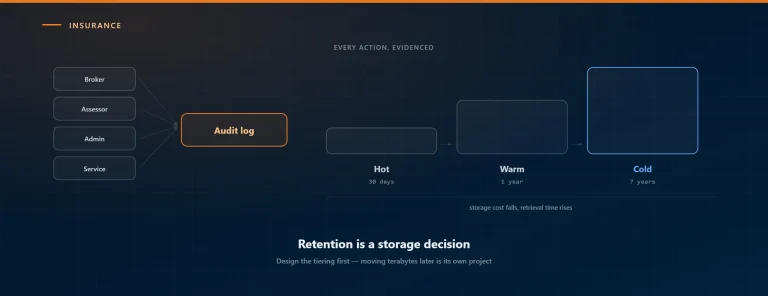
Automated where possible: configuration state, access reviews and change history collected continuously rather than assembled in the fortnight before an audit. Evidence gathered retrospectively is both expensive and weaker.
We look for a compensating control that meets the intent. Controls implemented against the grain of how people actually work get bypassed, and a bypassed control is worse than an acknowledged gap.
Three to nine months depending on starting maturity and scope. Anyone quoting a fixed number before looking at your environment is quoting a sales figure.
We empower your vision with innovative and effective strategies.
AI-powered assistant for services, careers & support
So we can assist you better